Detect and
stop rogue
AI agents
AI agents can act across files, networks and systems. We build the security layer that makes their actions visible, their risk explainable and intervention possible.
From one developer machine to the infrastructure around it.
* Reachability reflects account-level access; sensor coverage is reported separately.
Autonomy needs
an off switch.
An agent does not need malicious intent to cause harm. A compromised tool, a bad instruction or a mistaken action can cross a boundary fast. Security has to follow what the agent can reach and what it actually does.
Know what is running
Check executable identity and, where supported, installer provenance instead of relying on a process name alone.
See the real exposure
Separate declared permissions, observable activity and reachable resources. Show the evidence and the gaps in coverage.
Act with confidence
Give people a clear route from finding to investigation to intervention, with safeguards around the action itself.
Topgent.
A local view of the AI agents on your machine: what they are, what they can reach and when they need attention.
Topgent is our open-source starting point. It finds local agent processes, separates what they declare from what is observed and reachable, and shows the reasons behind a risk finding. Operators can stop a process after its identity is checked again. Analysis runs locally and collects metadata rather than prompts or file contents.
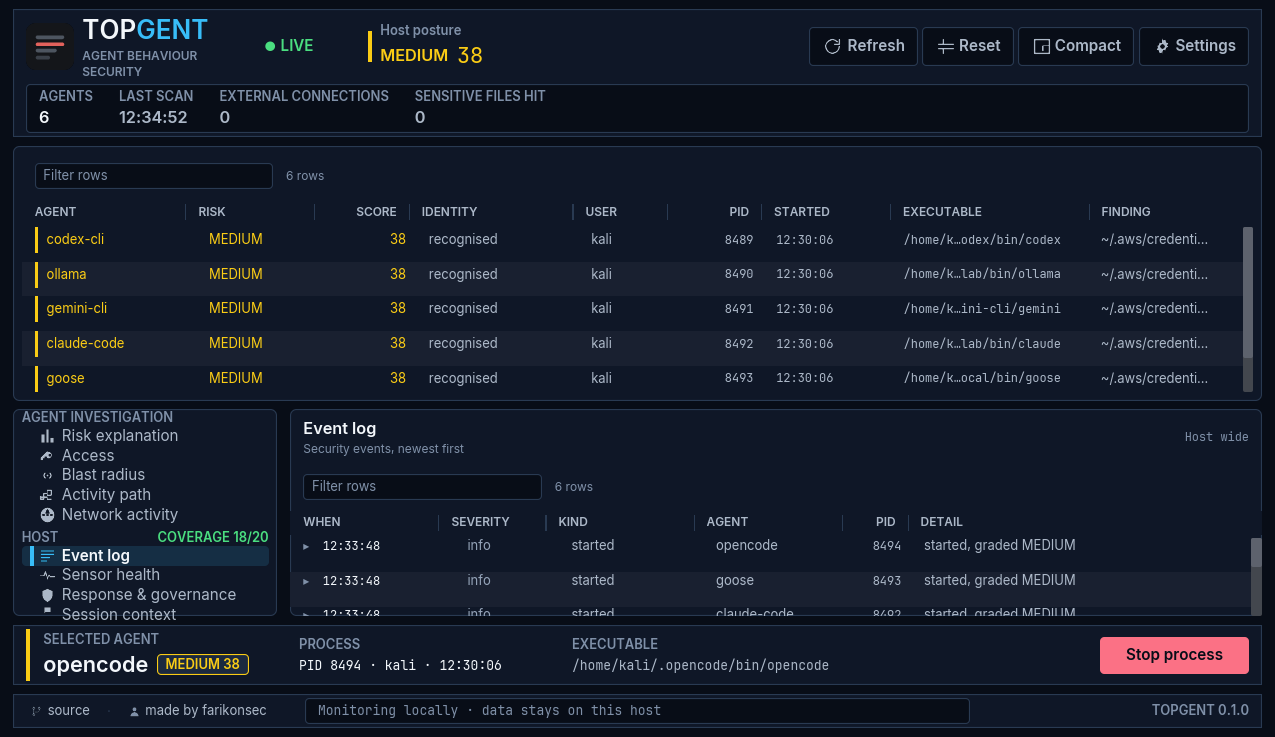
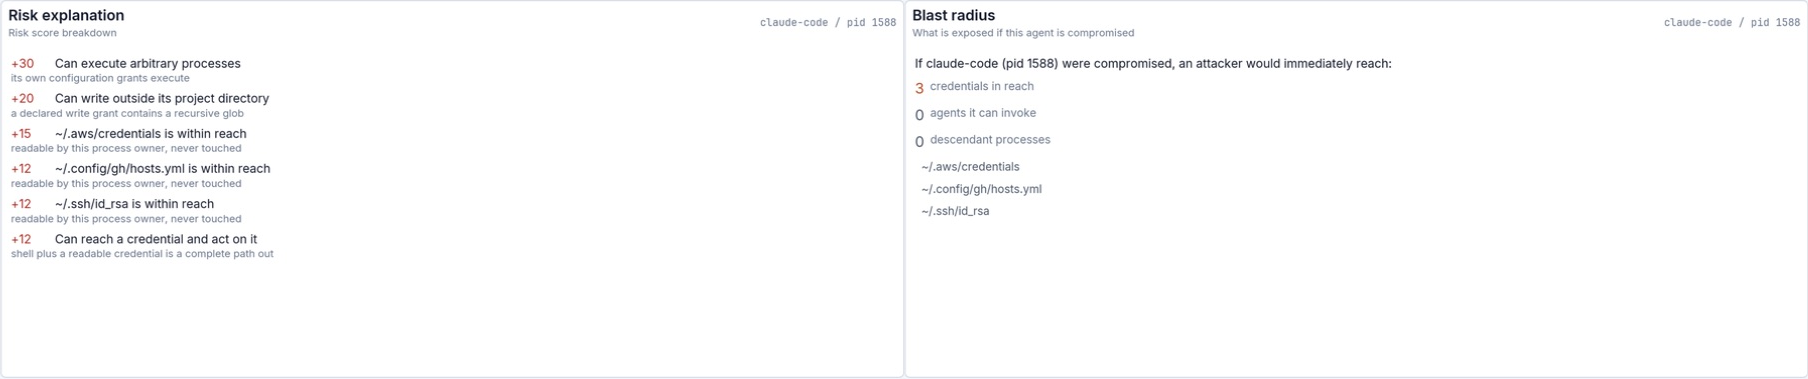
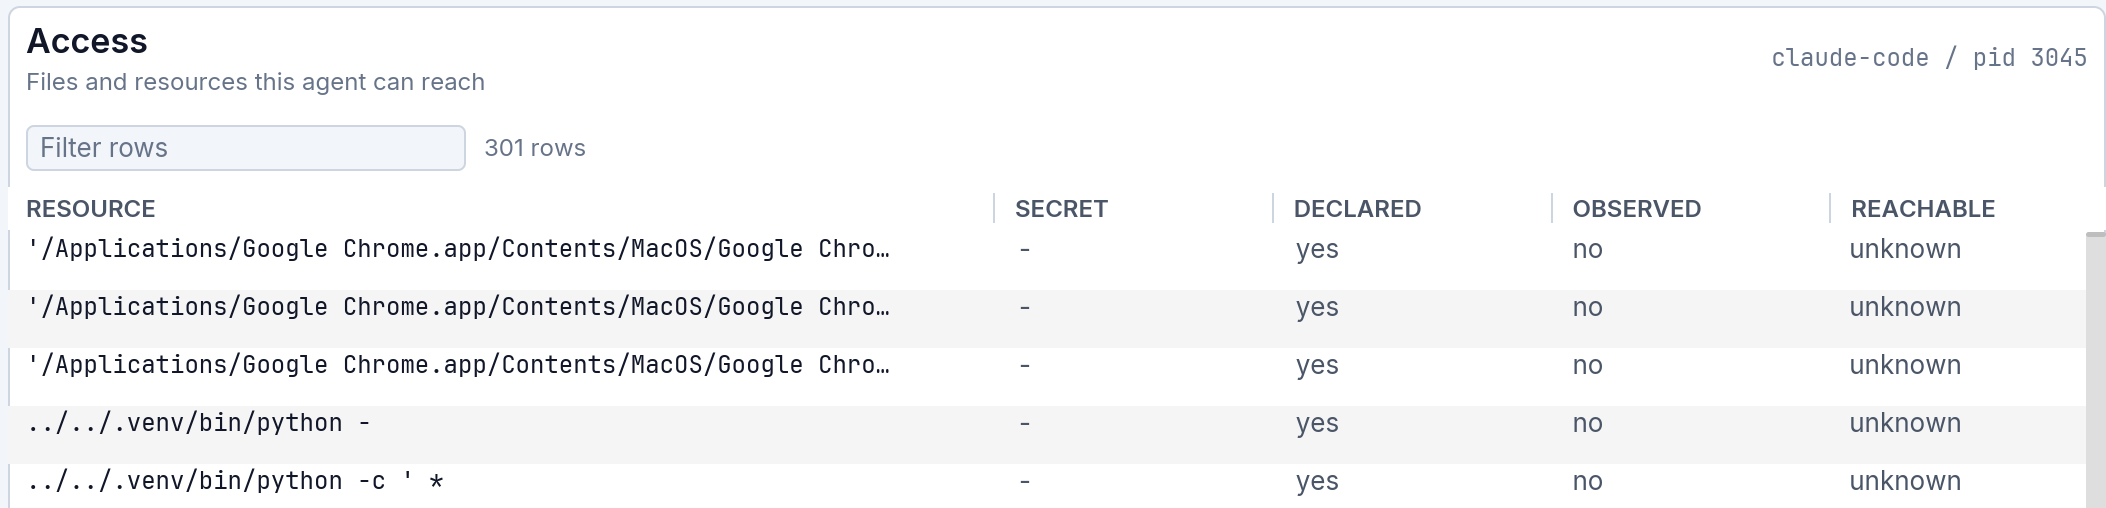
Product screenshots from the public Topgent repository; example sessions, not live site telemetry.
Security wherever
agents operate.
Topgent starts with local agents. The larger mission is protection that can travel with autonomous software across personal devices, enterprise estates and the infrastructure in between.
Personal devices
Clarity and control for the individual using AI tools every day.
Workstations
Visibility for developers and security teams as agents enter daily workflows.
Cloud & servers
Evidence and response for agents running in containers and production environments.
Embedded & edge
A long-term path toward security across more constrained and distributed systems.
These environments describe our direction, not a claim that Topgent currently supports each one.
Build the guardrails
before they’re missed.
We are looking for conversations with people who understand the security shift created by autonomous software.
Help shape the category.
We are building from a working open-source product toward a broader agent security platform. If that direction matches your thesis, we would like to compare notes.
Discuss investment or partnership ↗Bring a real problem.
Deploying agents in a team, product or sensitive environment? Tell us what you cannot see or stop today. Practical collaboration keeps the work honest.
Discuss a use case ↗The problem,
in 20 seconds.
A short introduction using real Topgent screenshots and an original soundtrack. On-screen text makes the story clear with sound off.
Let’s talk about
agent security.
We welcome investors, partners and practitioners who want to make autonomous systems safer to use.
Get in touchhello@caspiancrescent.com